Cyber Risk Management, Defined
Cyber risk management is the ongoing discipline of finding the cyber threats that could harm your organisation working out how likely and how damaging each one is and then reducing each to a level the business is willing to accept. It turns a vague sense of danger into ranked decisions with clear owners.
For most of its history cybersecurity was treated as a technical job for the IT team. That has changed. Under NIS2 and Sweden’s Cybersäkerhetslagen the board itself is now accountable for cyber risk and a serious incident lands as a legal and financial problem, not only an operational one.
The numbers explain the shift. The average data breach now costs 4.99 million US dollars worldwide, a record, according to the IBM Cost of a Data Breach Report 2026. Cybersecurity risk management is how you decide where a finite budget goes so the biggest exposures are covered first. In larger organisations it is also the core of what is called GRC or governance, risk and compliance.
How Cyber Risk Management Works
Every cyber risk management framework, whatever its name, is built on the same four stages. Learn the cycle once and any framework becomes easier to read.
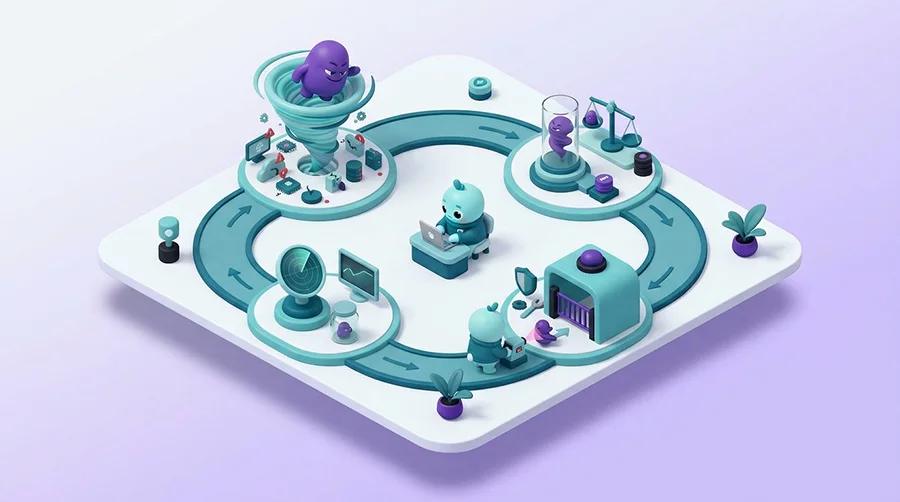
- Identify: Map what you have and what could go wrong. List the systems, data and suppliers that matter, then the threats and weaknesses that could hit them.
- Assess: Work out how likely each risk is and how much damage it would do then score and rank them so the worst rise to the top.
- Treat: Decide what to do about each risk. The four options are to reduce it, transfer it, accept it or avoid the activity that causes it.
- Monitor: Keep watching because assets, threats and the business all change. A risk assessment is a living record rather than a one-off report.
The reason this now needs its own discipline is scale. Cloud services, remote work, third-party software and AI have widened the attack surface faster than most teams can track by hand and regulators expect the work to be continuous rather than an annual audit.
Cyber Risk Management Frameworks
You do not have to invent a method. Several established frameworks give you a ready structure and most organisations combine two or three. The trick is knowing what each one is for.
- NIST Cybersecurity Framework (CSF) 2.0: A voluntary framework of six functions, Govern, Identify, Protect, Detect, Respond and Recover published by NIST in 2024. Its new Govern function puts board-level risk ownership at the heart of security which makes it good for organising a whole programme.
- NIST Risk Management Framework (RMF): The seven-step process in NIST SP 800-37, Prepare, Categorize, Select, Implement, Assess, Authorize and Monitor. It is more detailed and control-driven than the CSF and common where systems must be formally authorised to operate. This is usually what people mean by the NIST cyber risk management framework and it is not the same thing as the CSF.
- ISO/IEC 27001 and 27005: ISO 27001 is the certifiable standard for a risk-based information security management system and ISO 27005 is its companion guide for the risk work itself. Useful when you need independent proof for customers or auditors.
- FAIR: Factor Analysis of Information Risk, a quantitative model that expresses a risk as a probable financial loss rather than a high, medium or low label. Useful for putting a currency figure in front of a board.
- ISO 31000 and COSO ERM: The broader enterprise risk management frameworks that sit above the cyber-specific ones so cyber risk is reported in the same language as financial and operational risk.
None of these is a checklist you finish. They are structures for the four-stage cycle and the right choice depends on your sector, your size and what your regulators and customers ask you to prove.
The Business Impact of Getting It Wrong
Weak cyber risk management does not show up on a balance sheet until something breaks. When it does, the cost arrives on several fronts at once.
- Direct breach cost: The global average is now 4.99 million US dollars per breach, a record and up 12% in a year, per the IBM Cost of a Data Breach Report 2026. That covers investigation, recovery, lost business and legal work.
- Regulatory fines: Under NIS2 and Cybersäkerhetslagen, essential entities face fines of up to 10 million euros or 2% of global turnover. GDPR and DORA carry their own penalties on top.
- Downtime: Breaches now take a mean of 247 days to identify and contain, per the same IBM report, and revenue can stall for the worst of that stretch.
- Personal liability: NIS2 Article 20 makes the board not just the IT team, accountable for cyber risk.
- Supply-chain damage: IBM found supplier compromise to be the single costliest factor in a breach so a weak vendor can become your loss.
Risk management is the work that keeps these costs off your books. It will not remove every threat but it makes sure the money and effort you do spend land on the exposures most likely to hurt.
Real-World Cases
Four incidents show what unmanaged risk looks like in practice. Each traces back to a risk that could have been found and treated first.
Equifax and the Patch That Was Never Applied
The 2017 breach of the US credit agency Equifax began with a flaw in Apache Struts, a piece of web software. Apache had released a patch on 7 March that year and Equifax’s own security team had circulated an internal instruction to install it.
The patch was never applied to the online dispute portal. Attackers used the opening and moved through the network undetected for about 76 days, taking the personal data of roughly 147 million people.
The US Government Accountability Office later documented the basic failures behind it and Equifax settled with the FTC, the CFPB and 50 US states and territories for up to 700 million US dollars. The control that would have prevented it was mundane. Patch a known critical vulnerability quickly and confirm the fix is in place. A risk you have already spotted but left untreated is the most dangerous kind.
Change Healthcare and a Missing Second Factor
Change Healthcare processes about one in three medical claims in the United States. In February 2024 attackers logged into a remote-access portal using stolen credentials. The portal had no multi-factor authentication so a single password was enough.
Nine days later the ALPHV/BlackCat group launched ransomware across the systems. The company paid a 22 million US dollar ransom and because so much of US healthcare ran through this one provider, pharmacies and clinics felt the disruption for weeks.
In testimony to the US Congress the chief executive confirmed the missing multi-factor authentication and the US Department of Health and Human Services put the number of people affected at around 190 million. Two lessons stand out. Multi-factor authentication belongs on every external system and a supplier that everyone depends on is a concentration risk that has to be managed as one.
Miljödata and the Risk Inside a Supplier
In August 2025 Miljödata, a Swedish company whose HR and sick-leave software is used by around 80% of the country’s municipalities was hit by ransomware. The attackers got in through an outdated firewall component whose weaknesses were already public knowledge.
Because so many bodies relied on the same supplier, the incident reached more than 200 municipalities and regions. The Swedish data protection authority, IMY, later put the number of people whose data was exposed at 2.2 million, close to a fifth of Sweden.
In September 2026 IMY fined Miljödata SEK 1.8 million for failing to meet the security duty in GDPR Article 32. For every organisation that used the software, the lesson is that a supplier’s weakness is your risk too and that leaning the whole public sector on one vendor turns a single break-in into a national event.
Maersk and a Network With No Internal Walls
In June 2017 the shipping giant Maersk was caught in NotPetya, destructive malware that governments including the United States and the United Kingdom attributed to the Russian military. It spread across Maersk’s network in hours and wiped most of its computers and servers.
The malware moved so fast because the internal network was flat with few barriers to stop one infected machine reaching thousands. Maersk put the cost at around 250 to 300 million US dollars.
Recovery reportedly came down to a single server in an office in Ghana that had been offline during the attack and so kept a clean copy of key data. That was fortunate rather than planned. The controls that make recovery dependable are network segmentation to contain the spread and tested, isolated backups.
Cyber Risk Management and Compliance
In Europe cyber risk management is no longer only good practice. Several regimes now require it and each expects documented risk work rather than good intentions.
- NIS2 and Cybersäkerhetslagen: NIS2 Article 21 requires risk-management measures covering monitoring, incident handling, business continuity, supply-chain security and staff training. Article 20 makes the board personally accountable. Sweden’s version, Cybersäkerhetslagen (SFS 2025:1506), has been in force since 15 January 2026 and is supervised by MCF (formerly MSB) with fines up to 10 million euros or 2% of global turnover.
- DORA: For financial entities, DORA (Regulation 2022/2554) which applies from 17 January 2025, requires a formal ICT risk-management framework under Articles 5 and 6 with the management body accountable. In Sweden it is supervised by Finansinspektionen.
- GDPR: GDPR Article 32 requires security measures appropriate to the risk. The Miljödata fine was issued under this article which shows that a regulator can treat weak risk management as a breach in itself.
- ISO/IEC 27001: ISO 27001 certification is the usual way to prove a working risk-based security programme to customers and auditors and is often a condition of enterprise contracts.
The common thread is that all four ask you to identify your risks, act on them in proportion and be able to show your working. A risk register and a clear owner are the evidence each one wants to see.
How to Run a Cyber Risk Assessment
A cyber risk assessment is the practical heart of the whole discipline. It is how you turn a vague wish to be more secure into a ranked list of specific risks with owners. You can run a first pass in a workshop and refine it over time.
- Inventory what matters: List your important systems, data and suppliers. You cannot protect or rank what you have not written down.
- Identify the threats: For each asset, ask what could go wrong from ransomware and phishing to a supplier outage or a lost laptop.
- Score likelihood and impact: Rate how probable each risk is and how much harm it would do. A simple high, medium and low scale works to start and a quantitative model like FAIR adds a financial figure later.
- Rank and record: Put every risk in a register, sorted worst first each with a named owner and a planned response.
- Set your risk appetite: Agree with the board how much risk is acceptable so a decision to treat or accept a risk is deliberate.
Two honest warnings. Scoring is partly a judgement call so involve people who know the business, not only the IT team. And an assessment goes stale the moment it is filed because assets and threats keep changing. NIS2 Article 21 expects you to keep checking that your measures still work which is why the monitoring stage of the cycle never really ends.
How to Build a Cyber Risk Management Strategy
A cyber risk management strategy is what keeps the four-stage cycle running instead of stalling after the first assessment. It rests on people, process and technology and none of the three works alone.
- Give it an owner at board level: Cyber risk is a board responsibility under NIS2 so name who is accountable and report to them regularly. Where that seniority is missing in-house, a virtual CISO can carry it.
- Pick a framework and stick to it: Choose the NIST CSF, ISO 27001 or another that fits so your work has a common structure auditors recognise.
- Prioritise by business impact: Fix the risks that threaten your most important systems and data first not whichever alert is loudest.
- Manage suppliers as part of your risk: Know which vendors hold your data, track their security and plan for one of them being breached.
- Treat, transfer, accept or avoid on purpose: For each significant risk make a deliberate choice, whether that is a new control, cyber insurance, documented acceptance or dropping the activity.
- Monitor continuously and rehearse recovery: Watch for change, run continuous vulnerability management, test your backups and rehearse your incident response before you need it.
Done well, this is a programme, not a project. It will not make you immune but it means that when something does go wrong you have already decided who acts, what matters most and how you recover.