Threat Hunting Defined in Plain Terms
Threat hunting is the proactive search for attackers who are already inside your systems but have not yet triggered an alert. NIST defines it as proactively searching systems, networks and infrastructure for advanced threats to find and disrupt an adversary early rather than waiting for automated tools to raise the alarm.
Most organisations rely on tools that are reactive by design. Firewalls, antivirus, intrusion detection and a SIEM catch what matches a known signature or a written rule. The most capable intruders make sure they match neither.
That gap is why threat hunting exists. Also called cyber threat hunting or a cyber hunt, it assumes a breach has already happened and goes looking for it using human judgement and data rather than waiting for a warning that may never come. It is an active form of defence rather than another dashboard to watch.
How Threat Hunting Works
A hunt is not a random search. It follows a repeatable loop built on one working assumption, that an intruder may already be inside.
- Form a hypothesis. Start from a specific, testable idea about how an adversary might be operating often drawn from threat intelligence or a technique in the MITRE ATT&CK framework. For example, an attacker abusing PowerShell to move between machines.
- Gather and investigate. Pull the relevant data from endpoints, network telemetry, logs and the SIEM, then look for the behaviour the hypothesis predicts.
- Confirm or rule out. Decide whether the activity is really there. A hunt that finds nothing is still useful because it narrows where a real threat could hide.
- Respond and improve. Hand any confirmed compromise to incident response, then turn what you learned into a new automated rule so the next occurrence is caught without a human.
Good hunts also work backwards. Anything you can reliably detect with a rule should become a rule which frees the hunters to look for what no rule yet describes.
Types of Threat Hunting
Most hunts fall into three types. They differ by what sets them off, and mature teams use all three.
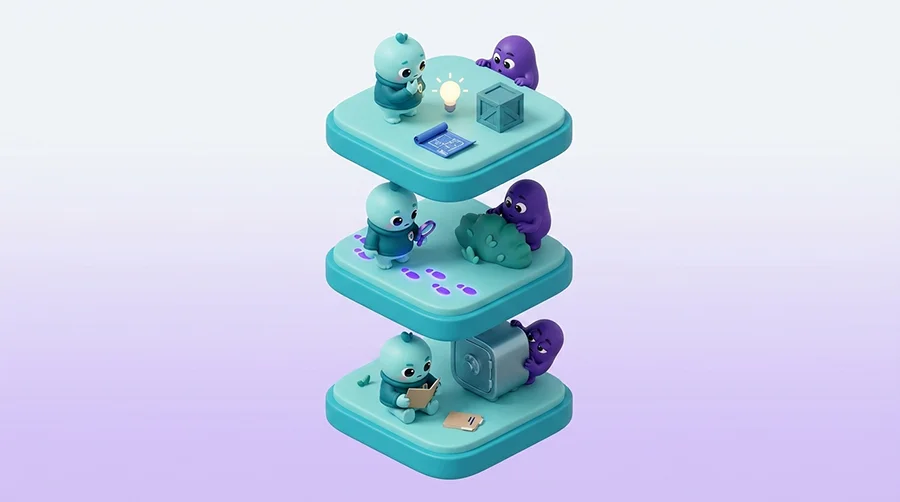
- Structured hunting: Driven by a hypothesis about attacker behaviour, usually mapped to a technique in MITRE ATT&CK. It looks for how an adversary acts rather than for one specific known file.
- Unstructured hunting: Triggered by an indicator of compromise or an anomaly already in the data for example an odd login or a flagged IP address. The hunter follows the thread to see what else is connected.
- Situational hunting: Shaped by risk and context such as intelligence that a group is targeting your sector or a review focused on your most valuable systems and accounts.
The type matters less than the habit. A team that only reacts to indicators will always be a step behind an attacker who brings none.
Why Threat Hunting Matters to the Business
The longer an intruder stays undetected, the more damage they can do, mapping the network, stealing credentials, finding the backups and positioning a payload. This window is called dwell time. In the Volt Typhoon case, a state-sponsored group kept access inside some victim networks for at least five years before discovery according to a 2024 CISA advisory.
Long dwell is possible because the strongest attackers avoid the things automated tools watch for. They use legitimate administrative tools and stolen but valid accounts so there is no malware to flag and no failed login to count. Hunting is the control designed to find that kind of quiet activity.
Finding an intruder early changes the outcome. An attacker caught during reconnaissance is an incident to clean up. The same attacker caught after they reach the backups is a business continuity crisis. Shortening the time to detection is the most direct lever an organisation has over the cost of a breach.
Real-World Cases
Three well-documented cases show why hunting earns its place. Each is drawn from official government reporting.
Volt Typhoon and Living Off the Land
In February 2024 CISA, the NSA and the FBI with Five Eyes partners, warned that a Chinese state-sponsored group tracked as Volt Typhoon had embedded itself in US critical infrastructure including communications, energy and water networks.
The group used living-off-the-land techniques, meaning legitimate built-in tools and valid stolen credentials rather than custom malware. That is why it stayed hidden. The agencies observed access in some IT environments for at least five years.
Signature-based detection had nothing to match. What surfaces this activity is hunting for anomalies in how trusted tools and accounts are used which is exactly what the advisory told organisations to do.
SolarWinds and the SUNBURST Backdoor
In December 2020 CISA issued Emergency Directive 21-01 after attackers slipped a backdoor called SUNBURST into a routine software update for the widely used SolarWinds Orion platform. Up to around 18,000 customers received the compromised update according to SolarWinds’ filing with the SEC.
The update was signed and trusted so nothing looked wrong. The US government later attributed the operation to Russia’s foreign intelligence service and CISA described a patient, well-resourced adversary that sustained long activity on victim networks.
A trusted vendor was the way in, so a rule for known-bad files was never going to help. The intrusion came to light through investigation of anomalous behaviour and hunting for unexpected outbound connections from trusted servers is the control that shortens this kind of discovery.
Target and the Alerts Nobody Acted On
In 2013 attackers reached the US retailer Target through credentials stolen from a third-party heating and cooling supplier then installed malware that skimmed payment cards at the till. Around 40 million payment card records and about 70 million customer records were exposed, according to a 2014 US Senate committee report.
The uncomfortable detail is that Target’s own monitoring detected the malware and raised alerts. No one acted on them in time.
Tools are only half of detection. The other half is a team with the time and mandate to investigate what the tools flag which is the human discipline hunting builds.
Threat Hunting and Compliance in Sweden and the EU
Swedish organisations do not have a free choice about detection any more. Cybersäkerhetslagen (SFS 2025:1506) came into force on 15 January 2026 and brings the EU NIS2 Directive into Swedish law.
Article 21.2a requires policies on risk analysis and information system security and Article 21.2b requires incident handling. Continuous, proactive monitoring is how organisations meet these duties and detect the intrusions that automated alerts miss.
The stakes are personal. Under Article 20 the board is responsible for these measures and can be held personally accountable. When an incident is confirmed the clock is short with an early warning to MCF (formerly MSB) and the sector authority within 24 hours, a full notification within 72 hours and a final report within a month.
Financial entities carry a parallel duty under DORA Article 17, supervised by Finansinspektionen and any personal-data breach must reach IMY within 72 hours under GDPR Article 33. Faster detection is what makes those deadlines survivable.
Threat Hunting and Incident Response
Threat hunting and incident response are often confused but they sit at opposite ends of the same timeline. Hunting is proactive. It goes looking for a threat before any alarm sounds. Incident response is reactive. It begins once a threat is confirmed.
The two connect at the handoff. When a hunt confirms a real compromise it becomes an incident and the response team takes over to contain, remove and recover. A hunt that finds nothing feeds the other direction sharpening the detections that trigger future response.
An organisation needs both. Relying only on incident response means you act after something has already gone wrong and often only once the damage is visible. Hunting buys back the time before that point.
How to Build a Threat Hunting Capability
Threat hunting rests on three foundations and a gap in any one limits the other two.
- People: Skilled analysts who understand attacker behaviour, can read forensic and log data and know how to form and test a hypothesis. This is the role of a threat hunter and it is scarce.
- Process: A regular hunting cadence with clear scope so hunts happen on a schedule and are not squeezed out by day-to-day alerts. Every finding feeds back into automated detection.
- Technology: Broad visibility into endpoints, network traffic and identity usually through EDR and a SIEM with logs retained long enough to investigate a slow intrusion.
A practical way to begin:
- Turn on and centralise your logs so endpoints, network and identity data land in one place a hunter can query.
- Adopt MITRE ATT&CK as a shared language for the techniques you hunt for.
- Assume breach. Run a first hypothesis-driven hunt on your most valuable systems rather than waiting for an alert.
- Convert every confirmed finding into a detection rule so the same thing is caught automatically next time.
- Decide honestly whether to build this in-house or have it run for you.
Building and keeping this capability in-house is demanding, which is why many Swedish organisations have hunting delivered as part of a managed detection and response service. The point is not who does the hunting. It is that someone is actively looking all the time.