Executive Summary
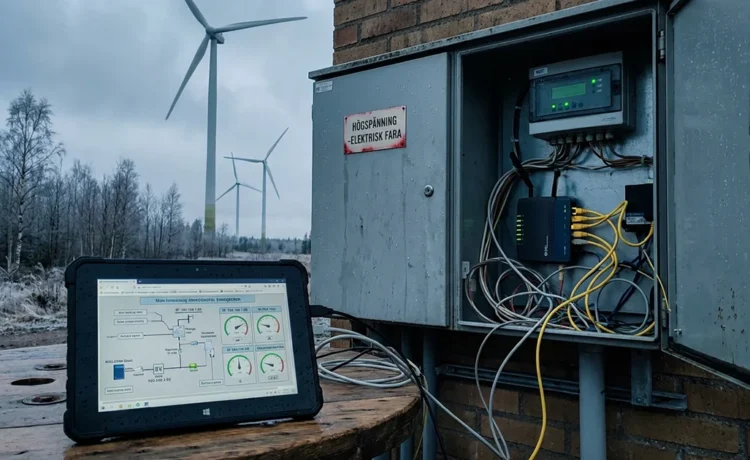
Industrial control systems exposed online in Sweden number in the thousands, according to an SVT investigation published on 12 October 2026. Using data from the search engine Censys, the public broadcaster found 3,809 IP addresses where control systems or their services were visible from the internet. In more than 2,000 of those cases SVT could see no protective layer such as a VPN, firewall or encryption. The exposed systems include supermarket refrigeration, IVF laboratories, wind turbine de-icing and ventilation in buildings used as polling stations. John Billow, head of Sweden’s National Cyber Security Centre (NCSC), said the agency shares SVT’s picture. No attack on the Swedish systems has been reported.
Industrial Control Systems Exposed With No Protective Layer
Of the unprotected addresses, 1,222 answered on industrial protocols used to monitor and talk to technical equipment. Another 865 had both a public web page and a direct link to industrial equipment. Most non-browser traffic ran over Modbus and BACnet, automation protocols with no login of their own. Anyone who reaches such a service can usually command the device directly.
In a Skövde building where Region Västra Götaland has offices, heating and ventilation could be controlled without any password, according to open data. The owner closed it after SVT called, saying a newer system alerts on anomalies so it judged there had been no risk.
Salem Takes 11 Building Systems Offline
In Salems kommun, 11 systems running municipal property were reachable with only a username and password. They covered heating and ventilation in schools and preschools that also served as polling stations, plus the ice rink’s operational alarm. More than 40 buildings had used the technology for up to about 15 years. After SVT’s questions the municipality said external access to operational monitoring had been shut down in every affected building.
Its auditors had raised governance gaps three years earlier. A KPMG review dated 20 September 2023 found the municipal executive board did not fully run systematic information security work. The adopted IT security plan dated from 2010 and the IT strategy from 2011. Interviewees said neither was current. Salem also had no information security coordinator which KPMG said was not in line with MSB recommendations. The audit didn’t examine building control systems.
Polling Stations and a Brewery Lab in Örebro County
Industrial control systems exposed in Örebro County included the Vågen and Krämaren shopping centres, a lab environment at Kopparbergs Bryggeri, an Eon site outside its plant area and refrigeration in five grocery stores. Owner Alecta Fastigheter said the centres ran older systems not yet moved to its new security network.
Vågen hosted early voting in the election.
SVT found exposed polling-station buildings in five counties. The Swedish Election Authority (Valmyndigheten) said vote reception was occasionally interrupted by alarms and fire alarms but it doesn’t know what triggered them. Nothing in SVT’s reporting links those alarms to an attack.
NCSC Says It Has Seen the Same Exposure
“We don’t recommend anyone expose systems this way,” Billow stated. Is a username and password enough? No, he said, “Something more is needed to secure your system.” NCSC already contacts critical infrastructure operators about exposures it sees and is analysing whether anything in the figures is particular to Sweden. CERT-SE linked the investigation in its weekly newsletter for week 42 on 16 October alongside advice from Luxembourg’s CSIRT, CIRCL, that cyber-physical systems should never face the internet.
A Night of Hijacked Fridges in France
SVT published the morning after attackers remotely raised temperatures in refrigeration linked to Danfoss at hundreds of French grocery stores which CERT-SE said destroyed food worth several million euros. Cyber insurer Coalition counted over 2,600 exposed refrigeration systems between September and October, many in France, Computer Sweden reported. SVT did not name the makers of the Swedish refrigeration it found. Its data doesn’t show whether anyone has logged in to any Swedish system.
Old Installations Behind Every Named Case
In September 2023 KPMG told Salem it lacked current security governance and an information security coordinator. Three years later it was found that 11 of its building systems were open to the internet. The audit did not cover building automation and nothing in the record ties the two together. What the named cases share is age. Salem, Alecta Fastigheter and the Skövde property owner each described their exposed systems as older installations.
References
- Granskning av Informationssäkerhet, Salems kommun
- CERT-SE:s veckobrev v.42
- Samhällsviktiga styrsystem ligger öppna på internet
- Nationellt cybersäkerhetscenter: ”Vi delar bilden”
- Salem stänger ner datasystem efter SVT:s granskning om stora risker
- Vallokal i Örebro har säkerhetsbrister
- Forskare hade varnat i månader innan hackare slog ut kylsystem i matbutiker
This post is also available in:
 Svenska