Executive Summary
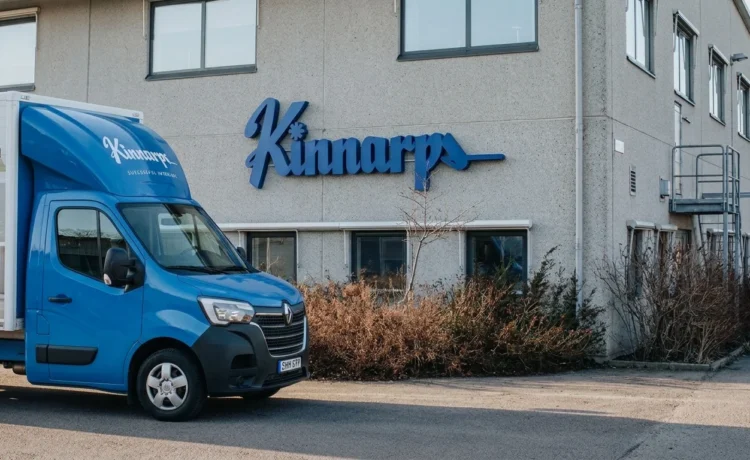
The Kinnarps cyberattack detected on the evening of Saturday 7 November 2026 has stopped production at three of the Swedish furniture manufacturer’s factories. Kinnarps AB shut down its systems and servers after finding abnormal activity in its network. Its plants in Kinnarp, Jönköping and Skillingaryd stood still from Monday 9 November. The stoppage affects 920 employees, according to a published report on 11 November. The company has filed a police report and says it has received no ransom demand. Who carried out the intrusion is unknown. Kinnarps has given no account of whether data was taken. On 10 November it hoped to restart production later the same week.
Which Factories the Kinnarps Cyberattack Stopped
The three idle plants are the three that the parent company runs itself. Kinnarps’ corporate information page lists six production facilities in Sweden, Kinnarp, Jönköping, Skillingaryd, Vinslöv and two in Tranås. The same page says Kinnarps AB is responsible for manufacturing at the first three. Kinnarps’ public statements mention only those three.
Kinnarps says 24 fully loaded containers leave its factories every day.
The group employs about 1,700 people, turned over SEK 4.0 billion in its 2024/2025 financial year and sells in around 40 countries. It is wholly family owned. Its delivery route planning is linked to production by its own description.
“It is serious, we are a large employer. It obviously affects our production because we depend on our systems,” said Ann Cederwall, Director Global Marketing & Communications at Kinnarps.
Detected on Saturday Evening and Stopped by Monday
Cederwall said the company found abnormal activity in its networks on the Saturday evening and shut its systems down at once to isolate the damage. By Monday morning visitors to the Kinnarps website met a notice that read, “We have disruptions in our IT system which mean our website is not working. We are working intensively to solve the problem.” Visitors were referred to the switchboard. The Kinnarps production halt covered all of Monday and Tuesday. On Wednesday, the fourth day, the lines were still down and 920 employees could not work, according to a published report.
“Since then our IT department, together with external experts, has worked extremely hard to limit and minimise damage. They were able to trace fairly quickly where the attackers got in and after that we filed a police report,” Cederwall said.
As of 10 November the servers were off while staff went through each device.
No Ransom Demand, No Named Attacker
Asked whether a ransom had been demanded, Cederwall answered that no demand had been made. Nobody has been named as responsible for the Kinnarps cyberattack. The company has not disclosed the entry point its experts traced. It gave no word on whether files were encrypted or copied. Nor has it stated whether personal data about employees or customers is involved.
That last point decides which clock runs. Under Article 33 of the GDPR, a personal-data breach must be notified to the Swedish Authority for Privacy Protection (IMY) within 72 hours of the organisation becoming aware of it. Kinnarps has not said whether it has made such a notification.
“It is too early to say whether something failed somewhere,” Cederwall said. The company’s stated hope on 10 November was to have production running fully again later that week.
Furniture Falls Outside the NIS2 Manufacturing Sector
Sweden’s cybersäkerhetslagen (2025:1506), in force since 15 January 2026, implements the NIS2 directive. Annex II of the directive limits its manufacturing sector to medical devices and NACE divisions 26 to 30, electronics, electrical equipment, machinery, motor vehicles and other transport equipment. Furniture manufacturing is division 31. On that reading, a stoppage that idled 920 people at a SEK 4.0 billion group triggers no 24-hour early warning to the national CSIRT. The only confirmed report is the one to the police. Kinnarps hasn’t stated whether it considers itself covered.
References
- Corporate Information
- Directive (EU) 2022/2555, Annex II
- EXTRA: 920 anställda kan inte jobba efter it-attacken
This post is also available in:
 Svenska