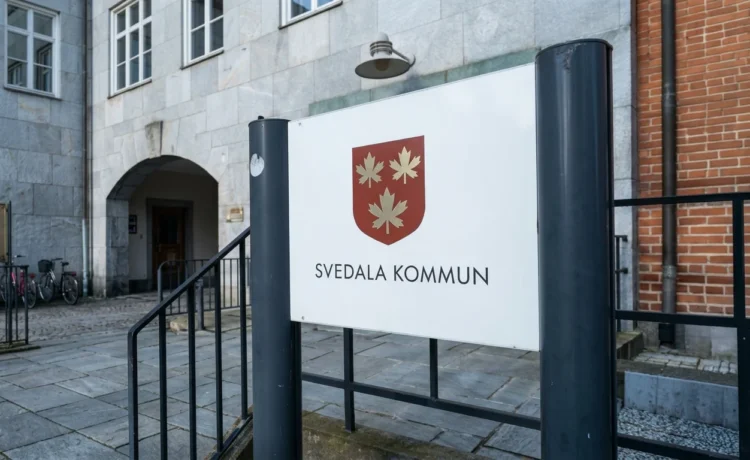
Svedala Municipality switched off every digital system it runs after an intruder got into its network overnight into Thursday 1 October. Municipal e-services stopped working and home care and elderly care staff moved to paper routines. Johan Lundgren, the municipality’s chief executive, told SVT the intrusion appears to be ransomware. No ransom demand had arrived.
The municipality, just south-east of Malmö, has gone into crisis mode and police are involved Sveriges Radio reported. There is no forecast for when systems will return. A temporary website carries updates and the switchboard is working.
The Shutdown Was Svedala’s Own Decision
According to SVT, someone got into the municipality’s IT systems and tried to access information. Svedala then took everything offline as a security measure. Lundgren told P4 Malmöhus it was an attack from outside but would not speculate about who was behind it or how they got in.
The shutdown has hit day-to-day services. E-services are down, care staff are documenting on paper and residents are directed to the switchboard. The municipality says it is still mapping the scope of the intrusion and cannot yet say what information may have leaked. TT reported that it is unclear whether sensitive information has ended up in the wrong hands.
Svedala runs social services, schools and elderly care. Operations are working well under the circumstances, according to Lundgren.
Risk Flagged in 2022 and Again in 2025
Svedala is working from a crisis management plan its executive board adopted in October 2025 according to the board’s November 2025 reply to the municipal auditors’ review of civil defence. Information security had come up before that. A 2022 review by KPMG for the auditors found that essential steps for managing information-security risks and requirements had not been carried out. Svedala’s annual report for 2025 lists IT security among the municipality’s risks citing growing dependence on digital systems. The planned response it gives is to strengthen IT security.
Neither document says how this intruder got in.
Reporting Deadlines Under the NIS2 Law
Swedish municipalities fall within Cybersäkerhetslagen (SFS 2025:1506), the Swedish NIS2 law in force since 15 January 2026. The government inquiry behind it proposed that every municipality be covered. According to MCF (formerly MSB), a significant incident must be reported in three stages, an early warning within 24 hours, an incident notification within 72 hours and a final report within one month.
Reporting so far does not say whether Svedala has classed the incident as significant or filed an early warning. Counting from the early hours of Thursday, the early warning was due in the early hours of Friday and the 72-hour notification falls due in the early hours of Sunday 4 October. GDPR sets the same 72-hour window for notifying IMY if personal data was affected.
Nine days before the attack, on 22 September, IMY fined Miljödata 1.8 million kronor for breaching Article 32.1 of GDPR. The Karlskrona software supplier was behind a large leak of personal data in 2025. IMY’s decision faulted it for lacking automatic real-time monitoring.
No Word Yet on Data, Entry Point or Attacker
Svedala has not said how the intruder got in or whether data left the network. No group has been named and Lundgren has given no timeline for restoring systems. Updates are going out on the temporary website.
References
- It-attack mot Svedala: kommunens digitala system ligger nere
- IT-attack mot Svedala kommun: ”Handbroms på allt”
- It-attack mot Svedala: ”Alla system nere”
- Yttrande över granskningsrapport avseende civilt försvar
- Granskning av informationssäkerhet
- Årsredovisning 2025 Svedala kommun
- SOU 2024:18 Nya regler om cybersäkerhet
- Konsekvensutredning för MCF:s föreskrifter om incidentrapportering
This post is also available in:
 Svenska