Key Takeaways
- One 24/7 seat needs 8,760 hours a year. A Swedish full-time analyst works about 1,880 hours after statutory leave, so five people is the floor for a single seat.
- Three analysts can cover 64 per cent of the year at best. Office hours from Monday to Friday are about 27 per cent of the week.
- At SCB’s average pay for IT security specialists plus 31.42 per cent employer contributions, five analysts cost SEK 4.56 million a year before pension, shift pay, a lead or any tooling.
- Under Cybersäkerhetslagen an early warning is due within 24 hours of becoming aware of a significant incident, weekends included. Reports have gone to FRA since 1 July 2026.
- Acceptable bids on one Swedish municipal SOC tender were about 3.6 times apart, so normalise scope before you compare any MDR quote.
- Buying MDR moves the work but not the accountability. IMY investigated two municipalities and a region after a supplier breach in August 2025.
Hiring Three to Five Analysts Buys Office Hours, Not a 24/7 SOC
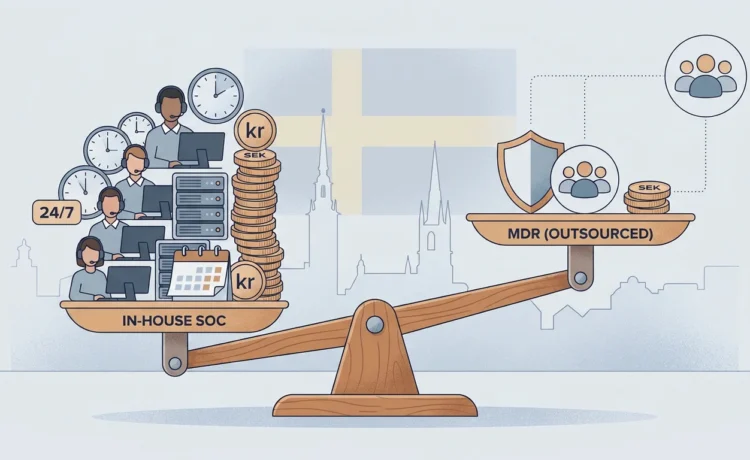
Since Cybersäkerhetslagen entered into force on 15 January 2026, many Swedish IT directors have had to tell their boards whether to build a security operations centre or buy one. The plan on the table is usually three to five analysts. Municipalities and regions face the same choice because the act covers them too. That headcount decides SOC cost in Sweden more than any licence does. It is also too small. Three to five people make a capable daytime team. They cannot keep one seat staffed every hour of the year.
The reason is a mismatch between how security teams were sized and when incidents now have to be handled. The old picture was a security function that worked office hours and read the alert queue on Monday morning. That still suits patching, projects and audits. What changed is the reporting clock. A significant incident now needs an early warning within 24 hours of the organisation becoming aware of it. A team that only watches in office hours is betting that awareness can wait until Monday.
MDR vs In-House SOC: What is the Difference?
Managed detection and response (MDR) is a service in which an external provider’s analysts monitor your environment around the clock, investigate alerts and take agreed response actions such as isolating a host. An in-house SOC delivers the same functions with your own staff, tooling and processes, so you carry every hour and every hire yourself.
Managed SIEM is narrower. It collects and correlates logs and forwards alerts, leaving investigation and response to you. Many organisations choose a hybrid in which a provider covers nights and weekends and an internal team owns daytime work.
How Many Analysts for a 24/7 SOC?
Start with the hours. One seat staffed around the clock is 8,760 hours a year. Arbetstidslagen caps ordinary working time at 40 hours a week and Semesterlagen gives every employee 25 days of leave. That leaves about 1,880 working hours per full-time analyst.
Divide one by the other and a single seat needs 4.7 people. Five is the floor. Five analysts leave only 640 hours a year for sick leave, training and public holidays. In practice that means one person alone at 03:00 with nobody on site to escalate to.
Rotas add constraints of their own. Arbetstidslagen also requires 11 hours of continuous daily rest and 36 hours of weekly rest, although collective agreements can adjust both. Three analysts deliver 5,640 hours (64 per cent of the year) even if nobody is ever ill. Office hours from Monday to Friday, 08:00 to 17:00, are about 27 per cent of the week.
The 24/7 Coverage Arithmetic
| One seat | 24 hours a day for 365 days is 8,760 hours a year. |
| One analyst | 2,080 contracted hours minus 25 days of statutory leave leaves 1,880 hours. |
| Three analysts | 5,640 hours (64 per cent of the year) with nobody ever sick. |
| Five analysts | 9,400 hours, leaving 640 hours for sick leave, training and public holidays. |
SOC Cost in Sweden: The In-House Floor
Salary is the largest line, so take it from the primary source. SCB’s salary search puts the average monthly pay for IT security specialists (SSYK 2516) at SEK 57,800, in figures SCB produced in 2024. The category covers all IT security specialists rather than SOC analysts alone, so treat it as a midpoint.
SOC Analyst Salary in Sweden and the Employer Cost
Skatteverket sets full employer contributions at 31.42 per cent of gross pay for 2026. On the SCB average one analyst costs SEK 911,529 a year in salary and statutory contributions. Five cost SEK 4.56 million.
That figure is a floor. It leaves out occupational pension, shift supplements, a SOC lead, recruitment and onboarding time. It also leaves out tooling such as a SIEM or log platform, endpoint detection and response, case management and threat intelligence, plus the engineers who keep detection rules current.
What Five Analysts Cost Before Tooling
| Monthly pay | SEK 57,800, the SCB average for IT security specialists. |
| Contributions | 31.42 per cent (SEK 217,929 per analyst). |
| Per analyst | SEK 911,529 a year. |
| Five analysts | SEK 4.56 million a year before pension, shift pay, a lead or tooling. |
What MDR Costs and How to Read a Quote
There is no public price list for MDR in Sweden and vendor-published ranges are not a neutral source. Public procurement is. Uppsala kommun’s award notice on TED, published on 19 December 2024, covers SOC as a service for the municipality and its companies from 1 November 2024 to 30 November 2028, with options to extend.
Eight bids came in. The lowest acceptable bid was SEK 24.59 million and the highest SEK 87.85 million, about 3.6 times apart for the same specification. Price carried 98 per cent of the award weighting. Quotes are not comparable until scope is.
Ask each provider to price the same scope. That means the telemetry covered, whether response actions or only alerts are included, the incident-response hours bundled and whether detection tool licences sit inside the price. Then hold every quote against the in-house floor of SEK 4.56 million for one staffed seat.
MDR for Mid-Market Companies and Municipalities
For a mid-market company with no security team, MDR buys round-the-clock coverage that five new hires would struggle to sustain. For an organisation that already employs two or three analysts, a hybrid is often the stronger option. The provider takes nights and weekends while the internal team keeps business context and daytime response.
Municipalities face the same arithmetic with procurement law on top. Uppsala kommun bought SOC as a service in 2024 and Sundsvalls kommun procured an MDR service in 2026, both through notices on TED.
Where Each Model Fits
- In-House SOC : Larger organisations with a security team already in place, strict data-handling constraints or detection needs specific to their own systems.
- MDR : Mid-market organisations with no analysts on staff that need round-the-clock detection and response from the start.
- Hybrid : Teams of two or three analysts who keep daytime ownership and buy coverage for nights, weekends and holidays.
MDR and NIS2 Compliance in Sweden
NIS2 does not require a SOC and does not mention 24/7 monitoring. Article 21 lists incident handling among the required risk-management measures and Article 23 sets the clock. An early warning is due within 24 hours of becoming aware of a significant incident, a fuller notification within 72 hours and a final report within one month.
In Sweden those duties sit in Cybersäkerhetslagen (2025:1506). On 1 July 2026 MCF (formerly MSB) transferred its cyber operations to NCSC at FRA. Notifications and incident reports now go to FRA. CERT-SE is organised within NCSC. MCF’s incident-reporting regulations, MCFFS 2026:8, applied from the same date.
MDR can make the 24-hour window achievable by detecting and triaging out of hours. It cannot own the decision that an incident is significant. Under Article 20 the management body approves the risk-management measures and can be held liable for failures.
Penalties Under Cybersäkerhetslagen
Essential entities face sanctions of up to EUR 10 million or 2 per cent of global annual turnover, whichever is higher. Important entities face up to EUR 7 million or 1.4 per cent. State agencies, municipalities and regions face a maximum of SEK 10 million.
Buying a Service Does Not Transfer the Accountability
Every outsourced service is a supplier risk. An MDR provider also holds privileged access to your environment. MCFFS 2026:11, in force from 1 October 2026, requires entities to assess and manage risks before outsourcing, to make sure suppliers take the measures compliance depends on and to keep evaluating them during the contract.
Miljödata, August 2025
Miljödata, an IT supplier whose HR systems many Swedish municipalities used, detected a cyberattack on 23 August 2025. Personal data on more than 1.5 million people was later published on the dark web. On 3 November 2025 IMY opened supervision of Miljödata and of two municipalities and one region that used its services. IMY later fined Miljödata SEK 1.8 million under GDPR Article 32(1).
The control that matters for an MDR buyer is the one IMY examined in the customers. That is documented supplier due diligence and contractual security requirements before data or access leaves your hands.
MDR Evaluation Checklist and RFP Questions
Put the same questions to every provider and score the answers rather than the brochure. Ask for evidence in writing, since the supplier assessment MCFFS 2026:11 expects is yours to document.
Questions to Put in Every MDR RFP
- Scope : Which endpoints, identities, cloud services and network logs are covered?
- Response : Which actions can the provider take without calling you?
- Out of hours : Who is on shift at 03:00 on a Sunday and how fast do they reach you?
- Reporting : Will the provider record the moment of awareness and help draft the early warning?
- Data : Where are logs stored, for how long and who can access them?
- Exit : How do you get your data, detection rules and case history back if you leave?
Building the SOC Business Case for the Board
Boards approve numbers they can audit. Lead with the cost of coverage rather than breach statistics from other countries. Show the in-house floor of SEK 4.56 million for one staffed seat, the share of the year three analysts can cover and each quote normalised to the same scope.
Then add the obligations the board owns directly. They include the 24-hour early warning, the management training MCFFS 2026:11 requires and the sanction band for your entity type. Justifying MDR spend is easier once the alternative is priced honestly.
The Line Every MDR Quote Has to Beat
Three to five analysts give you a strong daytime security team. They do not give you a 24/7 SOC. The people cost of even one staffed seat starts at SEK 4.56 million a year before tooling. Price that floor first. Normalise every MDR quote to the same scope, keep the supplier risk assessment on file and then decide.
Frequently Asked Questions
How many analysts do you need for a 24/7 SOC?
One seat staffed around the clock needs 8,760 hours a year. A Swedish full-time analyst works about 1,880 hours after 25 days of statutory leave, so five people is the floor for a single seat. That leaves only 640 hours for sickness, training and holidays.
How do you justify MDR spend to the board?
Price the alternative first. Show the in-house people cost of one 24/7 seat, SEK 4.56 million a year at SCB’s average pay, then compare provider quotes normalised to the same scope. Add the 24-hour NIS2 early warning and the sanction band the board is accountable for.
Does NIS2 require a 24/7 SOC?
No. NIS2 does not mention a SOC or 24/7 monitoring. It requires incident handling and an early warning within 24 hours of becoming aware of a significant incident, then a 72-hour notification and a one-month final report. Meeting that clock out of hours is where MDR or an on-call rota helps.
Can MDR replace an in-house SOC?
For round-the-clock detection and response it often can. MDR cannot replace your knowledge of the business, your decision that an incident is significant or management’s accountability under Cybersäkerhetslagen. Many organisations keep a small internal team for daytime work and use MDR for nights and weekends.
eBuilder Security offers MDR & SOC as a managed service. If you are pricing an in-house team against a provider, start with our MDR & SOC service page.
This post is also available in:
 Svenska