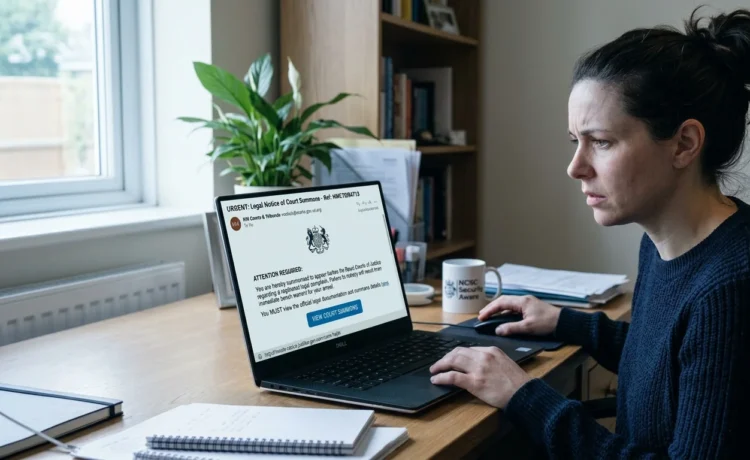
Emails claiming to deliver an “official warning from the court” and demanding a reply within 24 hours are circulating in the name of Sweden’s National Cyber Security Centre (NCSC). FRA and NCSC chief John Billow appear in the signature. NCSC said on 2 October that it is not behind the messages and that it only uses email addresses on the ncsc.se domain.
The Email NCSC Describes
NCSC’s notice describes a single template. The recipient is told they have received an official warning from the court and must respond within 24 hours, and the signature names Försvarets radioanstalt, FRA and John Billow. The government appointed Billow head of NCSC from 1 September 2025 and NCSC has been part of FRA since 1 November 2024.
NCSC has not said how many emails were sent, who received them or what a reply is meant to lead to. Its notice points readers to CERT-SE’s general advice on phishing.
NCSC’s Name Was Used a Year Ago Too
In the first week of October 2025, CERT-SE’s weekly newsletter reported that NCSC and MSB were both being named in phishing emails that asked recipients to make urgent cybersecurity updates, described as mandatory for all Swedish internet users. NCSC’s answer then matched this week’s, it was not behind the emails and it communicates from ncsc.se addresses.
Both campaigns borrowed the name of an agency that warns the public about online fraud. A message that appears to come from a cybersecurity authority can lower a recipient’s guard because it looks like the kind of warning people are told to take seriously. The named official makes this year’s email look specific and the 24-hour deadline leaves less time to check it.
October 2026: Tänk Säkert and MCFFS 2026:11
The new campaign coincides with Tänk säkert, the national information security campaign that runs every October. According to the police, NCSC holds main responsibility for it from 2026 taking over from MCF with the police as co-organiser.
It also arrived the day after MCFFS 2026:11 entered into force on 1 October. The regulation sets out security measures under Cybersäkerhetslagen. Chapter 3, section 10 obliges essential and important entities to gather information from NCSC at FRA and its national CSIRT so organisations in scope have a reason to read email from NCSC. Chapter 4, section 19 requires operators to identify and handle the need for others to verify their identity in digital channels and the general advice names email first.
NCSC’s statement that it only uses ncsc.se addresses is one such check. It depends on the recipient reading the full sending address because the display name and the reply-to address are the easiest parts of an email to forge.
As of 5 October, NCSC had not updated its 2 October notice.
References
- Nationellt cybersäkerhetscenters namn används i nätfiskekampanj
- Nätfiske
- John Billow ny chef på NCSC
- Om centret
- Tänk säkert: informationssäkerhetsmånad
- MCFFS 2026:11 Föreskrifter och allmänna råd om säkerhetsåtgärder och ledningens utbildning
- CERT-SE:s veckobrev v.40
- Nationellt cybersäkerhetscenter varnar för nätfiske
This post is also available in:
 Svenska