Executive Summary
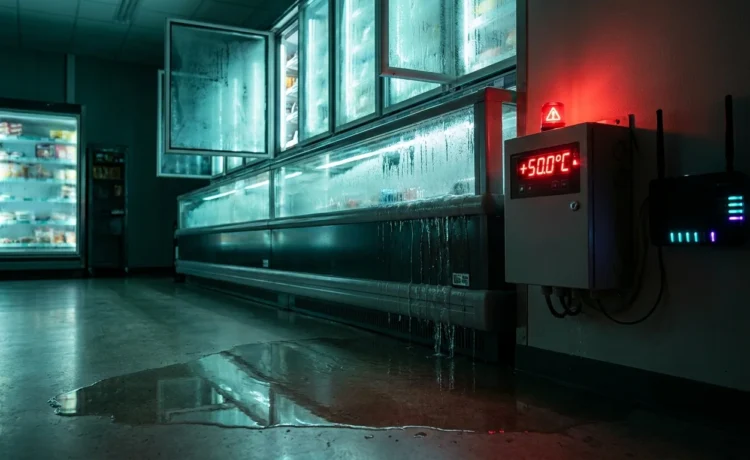
Freezers and chillers at several Swedish grocery stores were set to around 50°C overnight into Monday 2 November 2026 in an ICA and Coop cyberattack that destroyed chilled and frozen stock. ICA said a limited number of its stores were hit, among them ICA Kvantum Sjöbo, ICA Kvantum Tomelilla and ICA Nära Böda. Coop confirmed six affected stores in central Sweden. Neither chain has named the attacker or explained how the controls were reached. ICA says the stores connect outside its central network. Coop says its affected equipment is not from Danfoss, the manufacturer whose refrigeration controls were taken over in hundreds of French supermarkets on 12 October.
Freezers at 50°C in ICA and Coop Stores
ICA Kvantum Sjöbo in Skåne told customers on Facebook that its chillers and freezers had been hacked during the night and set to 50 degrees. Store manager Rickard Nilsson said staff couldn’t adjust the temperatures.
Everything was ruined, he said.
On northern Öland, ICA Nära Böda manager Mats Olsson arrived on Monday morning to a pool of water on the floor and a freezer reading 55°C. The store opened as usual with nothing chilled or frozen to sell. ICA Nära Sundbergs in Mörlunda closed until further notice after what it called a major chiller and freezer breakdown. At ICA Supermarket Brösarp, owner Mattias Liljegren said the attack was discovered at around 3 am.
Camilla Nilsson, who runs ICA Nära Sankt Olof, said her understanding was that someone had got into the settings of the store’s chillers and freezers and changed them.
Both Chains Point Away From Their Own Networks
“We know that a limited number of stores were affected by an incident during the night that affects their refrigeration and freezer systems,” ICA press officer Gustaf Nilsson said. ICA is supporting the stores but has given no store count. In a written comment published in Norway, Nilsson said the affected stores have their connection outside ICA’s central network according to a published report.
Coop press chief Carlos Cancino said in the same report that the attack came through a technical connection and did not involve Danfoss products. Coop had not contacted the police on Monday but didn’t rule out a report. Cancino called the financial damage limited so far.
Same Pattern Hit French Supermarkets in October
On the night of 11 to 12 October 2026, attackers took over refrigeration in hundreds of French supermarkets, including Intermarché, Coopérative U and Carrefour, forcing it into defrost. The Paris prosecutor’s office opened an investigation. France’s national cyber emergency team warned the same day about hijacked Danfoss store controllers and later added equipment from two other manufacturers. Danfoss said most of the affected French units were older products or had not been updated.
The target was the central controller that runs a store’s cooling, from temperatures to defrosting and alarms. Security researchers had already shown in August that these Danfoss units could be taken over remotely. Danfoss has since released fixes.
Danfoss controllers do run in Swedish Coop stores. A Danfoss Sweden news item from 7 December 2023 says Stora Coop in Lund upgraded its monitoring to a Danfoss system that went into service in November 2023. Lund is in Skåne. Coop places its six affected stores in central Sweden and says the equipment involved isn’t Danfoss.
Neither chain has said which brand of equipment or which service company sits behind the ICA and Coop cyberattack. They have also not said how the attackers got in or whether the units had been updated. No claim of responsibility had been reported by Monday. The link to France rests on how similar the two attacks look.
A Problem at the Store’s Own Connection
ICA puts the affected stores outside its central network. Coop points to a technical connection and rules out Danfoss. Both statements place the weak point at each store’s own remote link to its cooling equipment, operational technology (OT) rather than chain IT. That is the layer CERT-FR flagged in alert CERTFR-2026-ALE-012. The alert covered compromised Danfoss AK-SM and AK-SC system managers and later added Copeland XWEB and Dixell XWEB. A store that only checked its Danfoss equipment after 12 October would have missed both.
For Danfoss units the known flaws are documented. Claroty Team82 used CVE-2025-41451 for remote code execution on the AK-SM 800A, fixed in firmware R4.3.1. INCIBE-CERT lists an authentication bypass in AK-SM 8xxA versions before R4.2 caused by date-based password generation. The AK-SM850A that Stora Coop in Lund installed in 2023 falls within that 8xxA range.
References
- Freeze the Controller, Defrost the Food: Uncovering Vulnerabilities in Danfoss Refrigeration Controllers
- Dos nuevos avisos SCI y una actualización
- Sveriges första stora Optyma™ iCO₂ aggregat är i drift
- Published report
This post is also available in:
 Svenska