Executive Summary
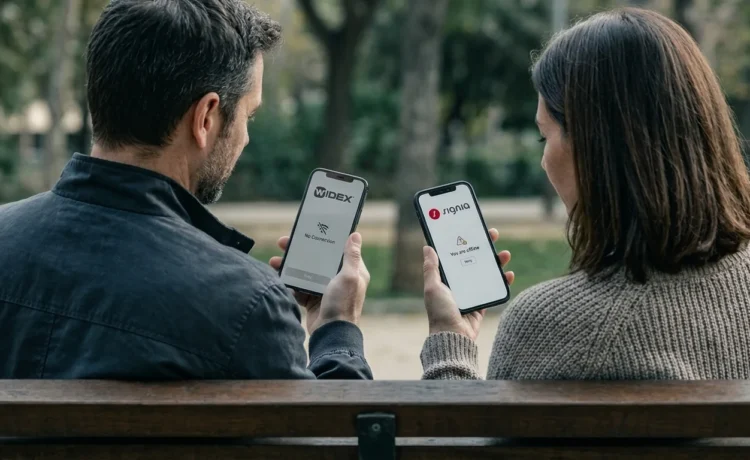
The WS Audiology cyberattack disclosed on 26 October 2026 involved unauthorised access to the customer relationship management (CRM) environment and certain operational systems of WSA, the Danish parent of the Widex and Signia hearing aid brands. WSA restricted access to some systems and brought in third-party forensic experts. Containment took the Widex MOMENT app, the Widex Compass Cloud fitting platform and Signia TeleCare offline. By 30 October WSA said Compass Cloud was working again and that the hearing aids themselves were never affected. The company has not named an attacker or said whether data was taken. It is WSA’s second disclosed intrusion since July 2024.
WS Audiology Cyberattack Reached the CRM Environment
WSA’s notice on its corporate site, dated 26 October, names the customer relationship management environment and certain operational systems as the areas accessed. WSA said it had contacted customers directly. The forensic investigation was ongoing.
The notice gives no date for when the intrusion began or was detected.
Four days later the wording shifted. In an updated statement on 30 October, published by a hearing industry trade site, WSA referred more broadly to unauthorised access to certain IT systems and said the incident related to its own IT environment. Core operations had kept running with interruptions from containment and systems were coming back in a phased and prioritised order.
Widex MOMENT, Compass Cloud and Signia TeleCare Taken Offline
The Widex MOMENT app, which wearers use to reach their hearing aid listening settings from a phone, was the service most affected according to WSA. The company expected it back over the weekend of 31 October and 1 November. It hasn’t said publicly whether that happened.
Widex Compass Cloud is the platform hearing care professionals use to fit and fine-tune Widex devices. WSA took it down as a precaution and said on 30 October it was fully functional again. A WSA spokesperson said the security threat “was not caused by our cloud-based software”. Signia TeleCare, a remote care service was due back early in the week of 2 November. Signia hearing aids could still be fitted and fine-tuned as usual.
WSA’s e-commerce sites stayed up and current orders were still being processed and shipped.
July 2024 Breach Ended in a Singapore Regulator Undertaking
On 5 July 2024 WSA identified unauthorised access to the local retail IT system of its Bloomhearing stores in Australia and New Zealand which also held some Hong Kong and Singapore retail data. In a 10 September 2024 update, WSA said the threat actors had temporary access to personal data of hearing aid patients and employees and may have copied it.
Singapore’s Personal Data Protection Commission (PDPC) later described that event as a ransomware attack on archived data stored on a server of Active Hearing, WSA’s Australian retail arm. Widex Singapore notified the regulator on 15 July 2024 and the PDPC accepted a voluntary undertaking from Widex Singapore, executed on 22 April 2025 and published on 21 May 2025. It commits the company to moving all personal data held on Active Hearing’s systems back to the Singapore data centre.
Neither of WSA’s 2026 statements refers to the 2024 incident.
Attacker, Entry Point and Data Still Unnamed
WSA has not named a threat actor behind the WS Audiology cyberattack or said how the attackers got in. It gave no count of affected customers and did not say whether the CRM environment held personal data that was viewed or copied. No indicators of compromise have been published. Nor has WSA said whether it notified Denmark’s Datatilsynet or any national cybersecurity authority.
The NIS2 Directive covers manufacturers of medical devices under the EU Medical Device Regulation in its Annex II. Article 23 requires an early warning to the national CSIRT within 24 hours of a significant incident becoming known. WSA’s statements do not address NIS2.
67 Days to Confirm Data Access in 2024
In 2024 WSA identified the Bloomhearing intrusion on 5 July. Its Singapore unit told the PDPC 10 days later. Public confirmation that patient and employee data had been accessed came in the 10 September update, 67 days after detection. This time the first notice named the CRM environment, the system where a company keeps its customer records, on day one. Eight days on, WSA had said nothing about what that environment held or whether any of it left the network.
References
- Information about IT security incident
- IT security incident update
- Voluntary Undertaking by Widex Singapore Pte Ltd
- Directive (EU) 2022/2555
- Published report: WSA statement of 30 October 2026
This post is also available in:
 Svenska